Agentic compliance
Map once. Comply everywhere. Run easy.Compliance, from your first ISO 27001 or SOC 2 to a complete GRC program.
Our agents identify what applies to you and get it done. You make the calls.
ISO 27001 · SOC 2 · TISAX® · NIS2 · DORA · CRA · EU AI Act · ISO 42001 · GDPR
Agents
Agents that do the compliance work, with you in charge
GetTeddy's agents run the recurring work inside your connected systems. Every output is versioned and traceable, so your auditor can follow it.
Certification Agent
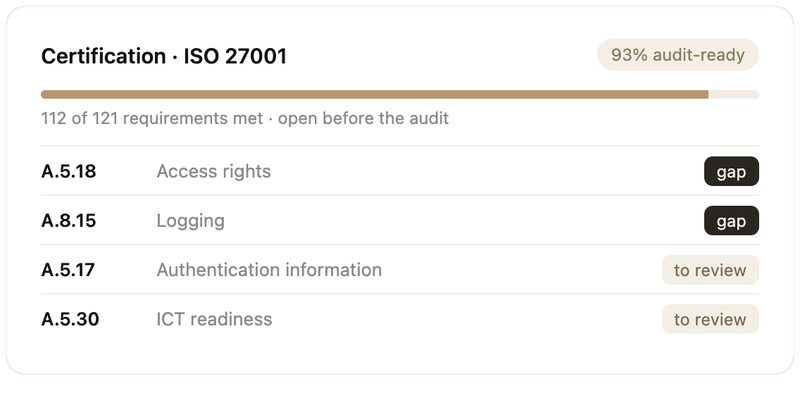
Your path to a first ISO 27001 or SOC 2 Type II, step by step
Gap Audit Agent
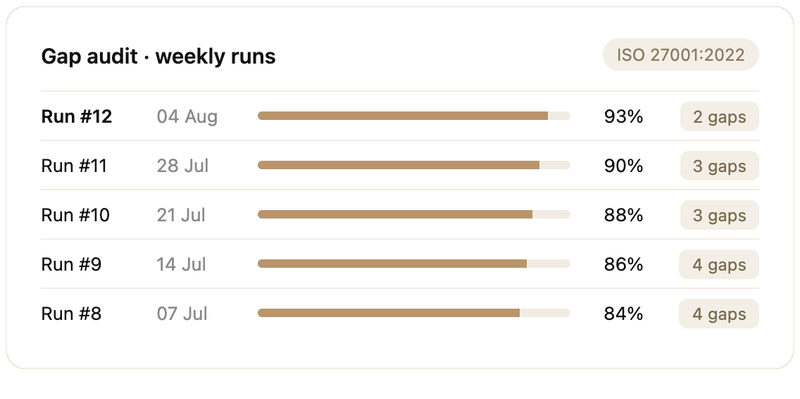
A complete gap audit in minutes, daily or weekly
Evidence Agent
Collects evidence on schedules and maps it to every control
Policy Agent
Drafts policies from your real systems, in the languages your teams work in
Certification Agent
Explains what to do next and tracks every open step until the auditor arrives.
Gap Audit Agent
Audits your whole company in minutes, daily or weekly, so new gaps surface right away instead of once a year.
Evidence Agent
Pulls evidence from your cloud, identity and HR tools and flags anything stale.
Policy Agent
Writes policies that match how you actually work, and flags drift.
How it works
One model of your company. Every regulation mapped onto it.
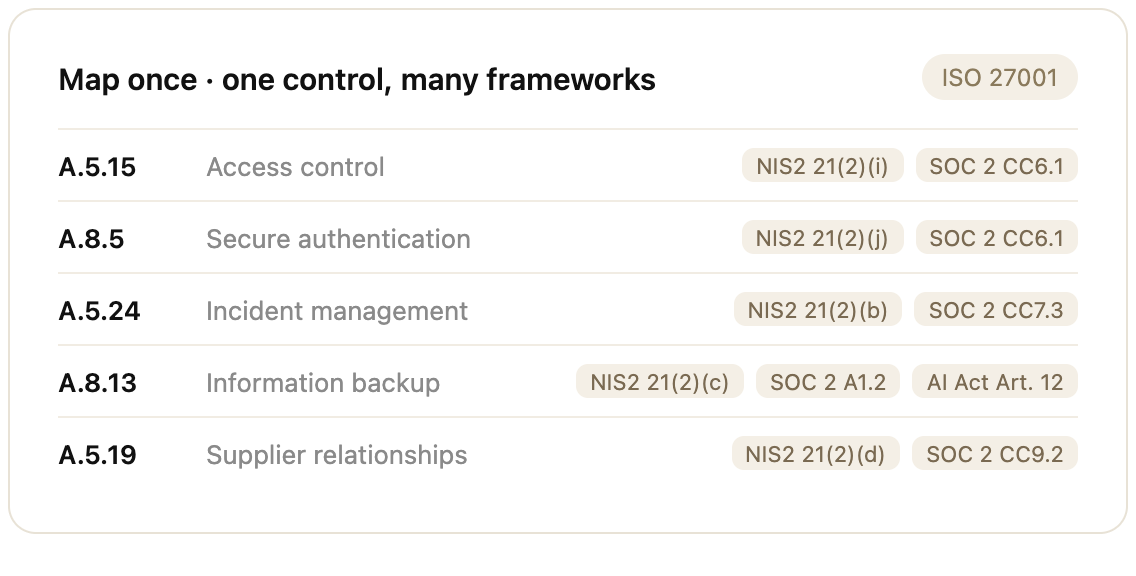
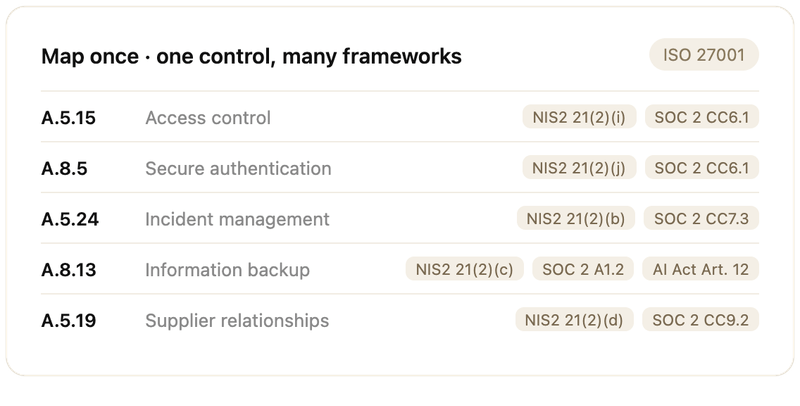
Describe your company once. GetTeddy maps every framework that applies and reuses each control and piece of evidence across all of them.

Map once
One company model
Comply everywhere
Multiple frameworks, one control set
Controls
Policies
Evidence
Contracts
Integrations
Connected to the stack you already run
GetTeddy collects evidence from your cloud, identity, HR and developer tools, so agents work on real data. Missing a system? GetTeddy offers custom integrations.
FAQ
Questions CISOs ask us
What the agents do, who approves their work and how your data is protected.
What is GetTeddy?
GetTeddy is an agentic compliance platform. It builds one model of your company, maps every regulation that applies and runs the recurring work with AI agents: evidence, gap audits, policies, questionnaires and contract reviews.
Which frameworks does GetTeddy cover?
ISO 27001, SOC 2, TISAX®, NIS2, DORA, CRA, the EU AI Act, ISO 42001 and GDPR, all on one control set. When you add a framework, GetTeddy starts from the coverage you already have.
What do the agents do on their own?
They collect evidence, run gap audits, draft policies, answer questionnaires and review contracts. Every task is labelled as automated, agent-drafted and human-approved, or yours.
What stays with my team?
Every decision. Scope, risk acceptance, policy approval, answers sent to customers and management sign-off always stay with a named person.
How is GetTeddy different from a compliance checklist tool?
Checklist tools track the work. GetTeddy's agents do it. One company model and one control set cover security, privacy, AI and product rules together, so nothing is done twice.
How do you protect my data?
With tenant isolation, encryption in transit and at rest, and a public subprocessor list. Our security page explains every measure in detail.
Do you train AI models on my data?
No. Your data is never used to train models.
Can I see what the agents did?
Yes. Every agent run is recorded in the action log with its inputs, its output and the person who approved it, so auditors can trace each result back to its source.
Can I control what each agent may do?
Yes. You set an owner, the permissions and a kill switch for every agent.
Which systems does GetTeddy connect to?
Identity providers, cloud platforms, HR systems, code repositories and device management. If a system you run is not on the list, GetTeddy offers custom integrations.
How does onboarding work?
A compliance engineer sets up your workspace with you, connects your systems and imports your existing documents. The agents start working as soon as the first systems are connected.
Can I switch from another tool?
Yes. GetTeddy imports your controls, policies and evidence from Vanta, Drata or spreadsheets, and a compliance engineer leads the cutover.
How is GetTeddy priced?
By how much work the agents take on, from one framework to multi-entity programs. Book a demo and we’ll prepare a quote for your setup.
Do I still need an auditor?
Yes. For ISO 27001, an accredited certification body decides on certification. For SOC 2, a licensed CPA firm issues the report. GetTeddy prepares the audit package and gives your auditor structured access to the evidence.
How do I get started?
Book a demo. We look at your setup together and show the agents working on your frameworks.